News
Kaspersky Warns Of Rising Cookie Hijacking Threat
A new report highlights how session hijacking through cookies could expose users to identity theft, financial loss, and account compromise.


Cookies are a familiar part of modern browsing, powering everything from saved logins to personalized settings. But according to a new Kaspersky report, they’re also a growing security risk. The study found that 87% of surveyed websites display cookie notifications, yet most users remain unaware of how these files can be exploited by attackers through a process known as session hijacking.
Cookies are small text files stored in browsers, often containing preferences, personal data, or even login credentials. If compromised, attackers can steal a user’s session ID and gain access to active accounts. Once inside, they could perform unauthorized actions such as retrieving payment information, placing fraudulent orders, or sending malicious communications.
Attackers have several methods to exploit cookie data. On unsecured HTTP sites or public Wi-Fi networks, session sniffing can intercept IDs in real time. Cross-site scripting (XSS) injects malicious code into a site to extract cookie data directly from the browser. Session fixation tricks users into authenticating with a pre-set session ID, allowing attackers to gain control after login. In practical terms, this could expose sensitive details such as shipping addresses, payment settings, or even lead to full account takeover.
“Cookies are the backbone of seamless online experiences, enabling everything from personalized settings to streamlined logins, but they’re also a target for hackers if not handled with care,” said Natalya Zakuskina, Senior Web Content Analyst at Kaspersky. “Without proper safeguards, attackers can exploit session IDs to hijack user accounts, steal sensitive data, or even manipulate website interactions, making it imperative for developers to prioritize security measures and for users to stay proactive in protecting their digital footprint”.
Also Read: KAUST Mathematical Model Tackles 5G Interference With Aircraft
Kaspersky advises users to avoid entering sensitive data on HTTP-based sites, minimize cookie acceptance, and regularly clear cookies and cache. Additional precautions include using VPNs on public Wi-Fi, enabling two-factor authentication, and steering clear of suspicious links.
With cookies underpinning so much of the digital economy, Kaspersky warns that ignoring these vulnerabilities could result not only in financial losses but also long-term reputational damage for individuals and businesses alike.


News
NEOPAY Wants To Follow Merchants Across Channels And Borders
A controlling 65% stake in noon payments would give NEOPAY access to marketplace sellers, online merchants and the payment flows they generate.
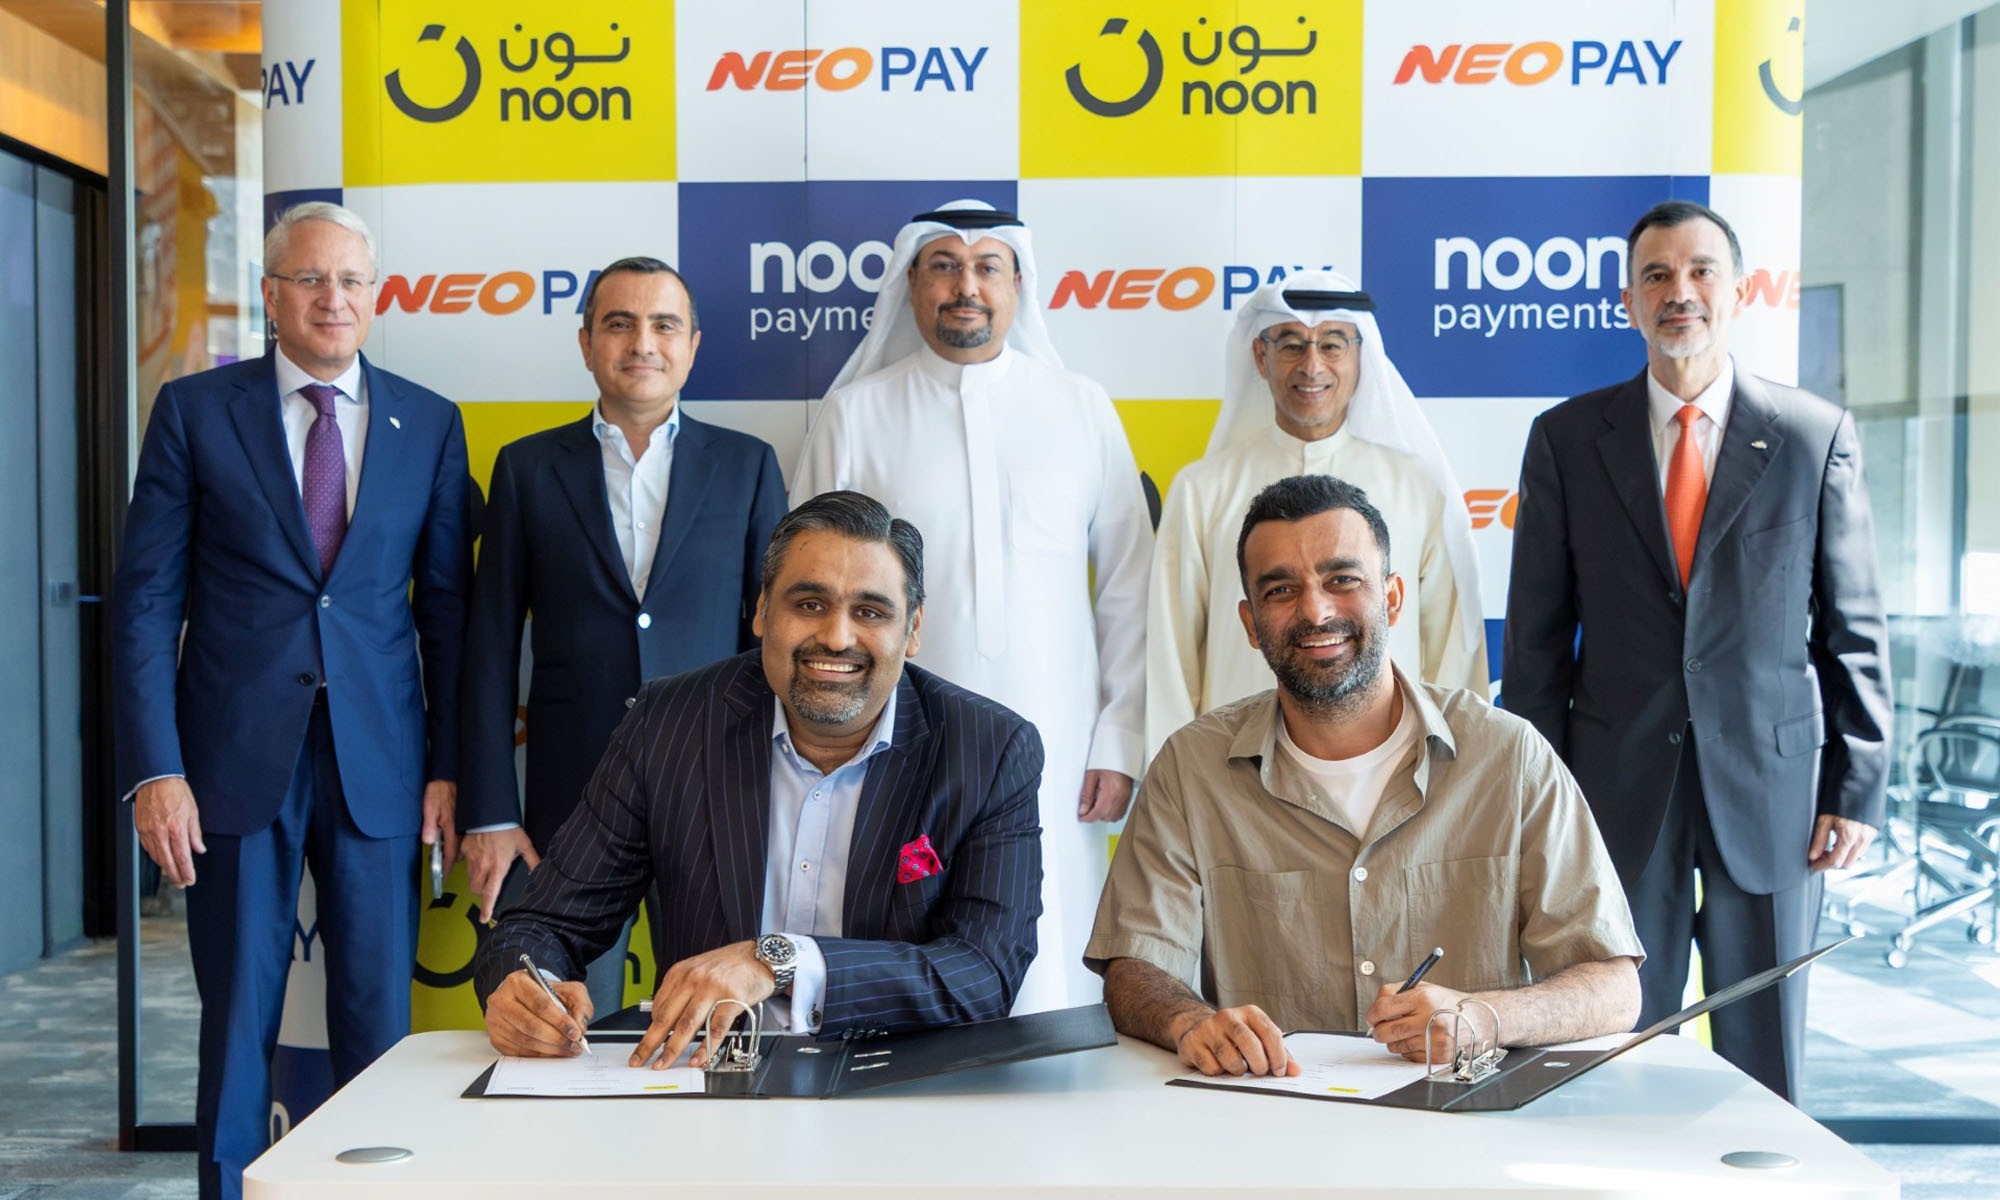
It’s been a long time since checkouts were single defined places. A merchant might take payments at a physical register, on its own website and through an online marketplace, sometimes in more than one country. NEOPAY wants to follow those transactions wherever they happen.
The UAE payments company has entered into an agreement to acquire a 65% controlling stake in noon payments. NEOPAY already runs the acquiring infrastructure that lets merchants accept card payments, along with omnichannel acceptance and a merchant services platform. This new deal would add noon payments’ embedded payments platform, e-commerce gateway and merchant network across the UAE, Saudi Arabia and Egypt. That would considerably expand both NEOPAY’s digital commerce capabilities and its regional reach.
For merchants, the attraction is a single provider for online and in-store payments, plus faster settlements, data and analytics, and value-added financial services.
“Payments should be simple, reliable, and built for the markets they serve,” said Faraz Khalid, CEO of noon. His counterpart at NEOPAY, Vibhor Mundhada, added: “We have built a strong payments business in the UAE, and our ambition is now to take that capability across the region”. The acquisition, Mundhada added, would “expand our footprint into Saudi Arabia and Egypt” while reinforcing NEOPAY’s position at home.
Also Read: In Kuwait, Your Surgeon Might Be Operating From Another Country
NEOPAY is also keen to point out potential payment volume increases. The company says noon payments’ integrations with marketplace sellers and online merchants create high transaction density in some of the region’s fastest-growing digital commerce segments. It also believes control of the business would give it access to those merchant relationships and payment flows, and speed up the rollout of alternative payment methods and installment options.
The combined roadmap targets faster merchant onboarding, better payment performance, tighter fraud controls and embedded financial services. The deal could also strengthen cross-border payments and settlement along key regional commerce corridors.

NEOPAY Wants To Follow Merchants Across Channels And Borders

RØDE’s Low-Profile Studio Arm Is Designed To Stay Out Of Shot

Microsoft Plans $10 Billion-Plus Gulf Expansion Despite Iran Conflict

In Kuwait, Your Surgeon Might Be Operating From Another Country

Qatar Folds 45 State Companies Into A Single Investment Platform

Trip.com Is Betting An AI Agent Will Book Your Next Vacation

Apple’s First Folding iPhone Arrives Late To A Shrinking Market

Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power

Musk’s Boring Company Wants To Dig 150 KM Of Tunnel Under The UAE

OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA


-
 News3 weeks ago
Trip.com Is Betting An AI Agent Will Book Your Next Vacation
-
 News3 weeks ago
Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power
-
 News3 weeks ago
Musk’s Boring Company Wants To Dig 150 KM Of Tunnel Under The UAE
-
 News3 weeks ago
OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA