News
Beirut Airport Cybersecurity Incident: How It Unfolded
On Sunday January 7, Rafic Hariri International Airport’s screens began displaying political messages instead of flight information.

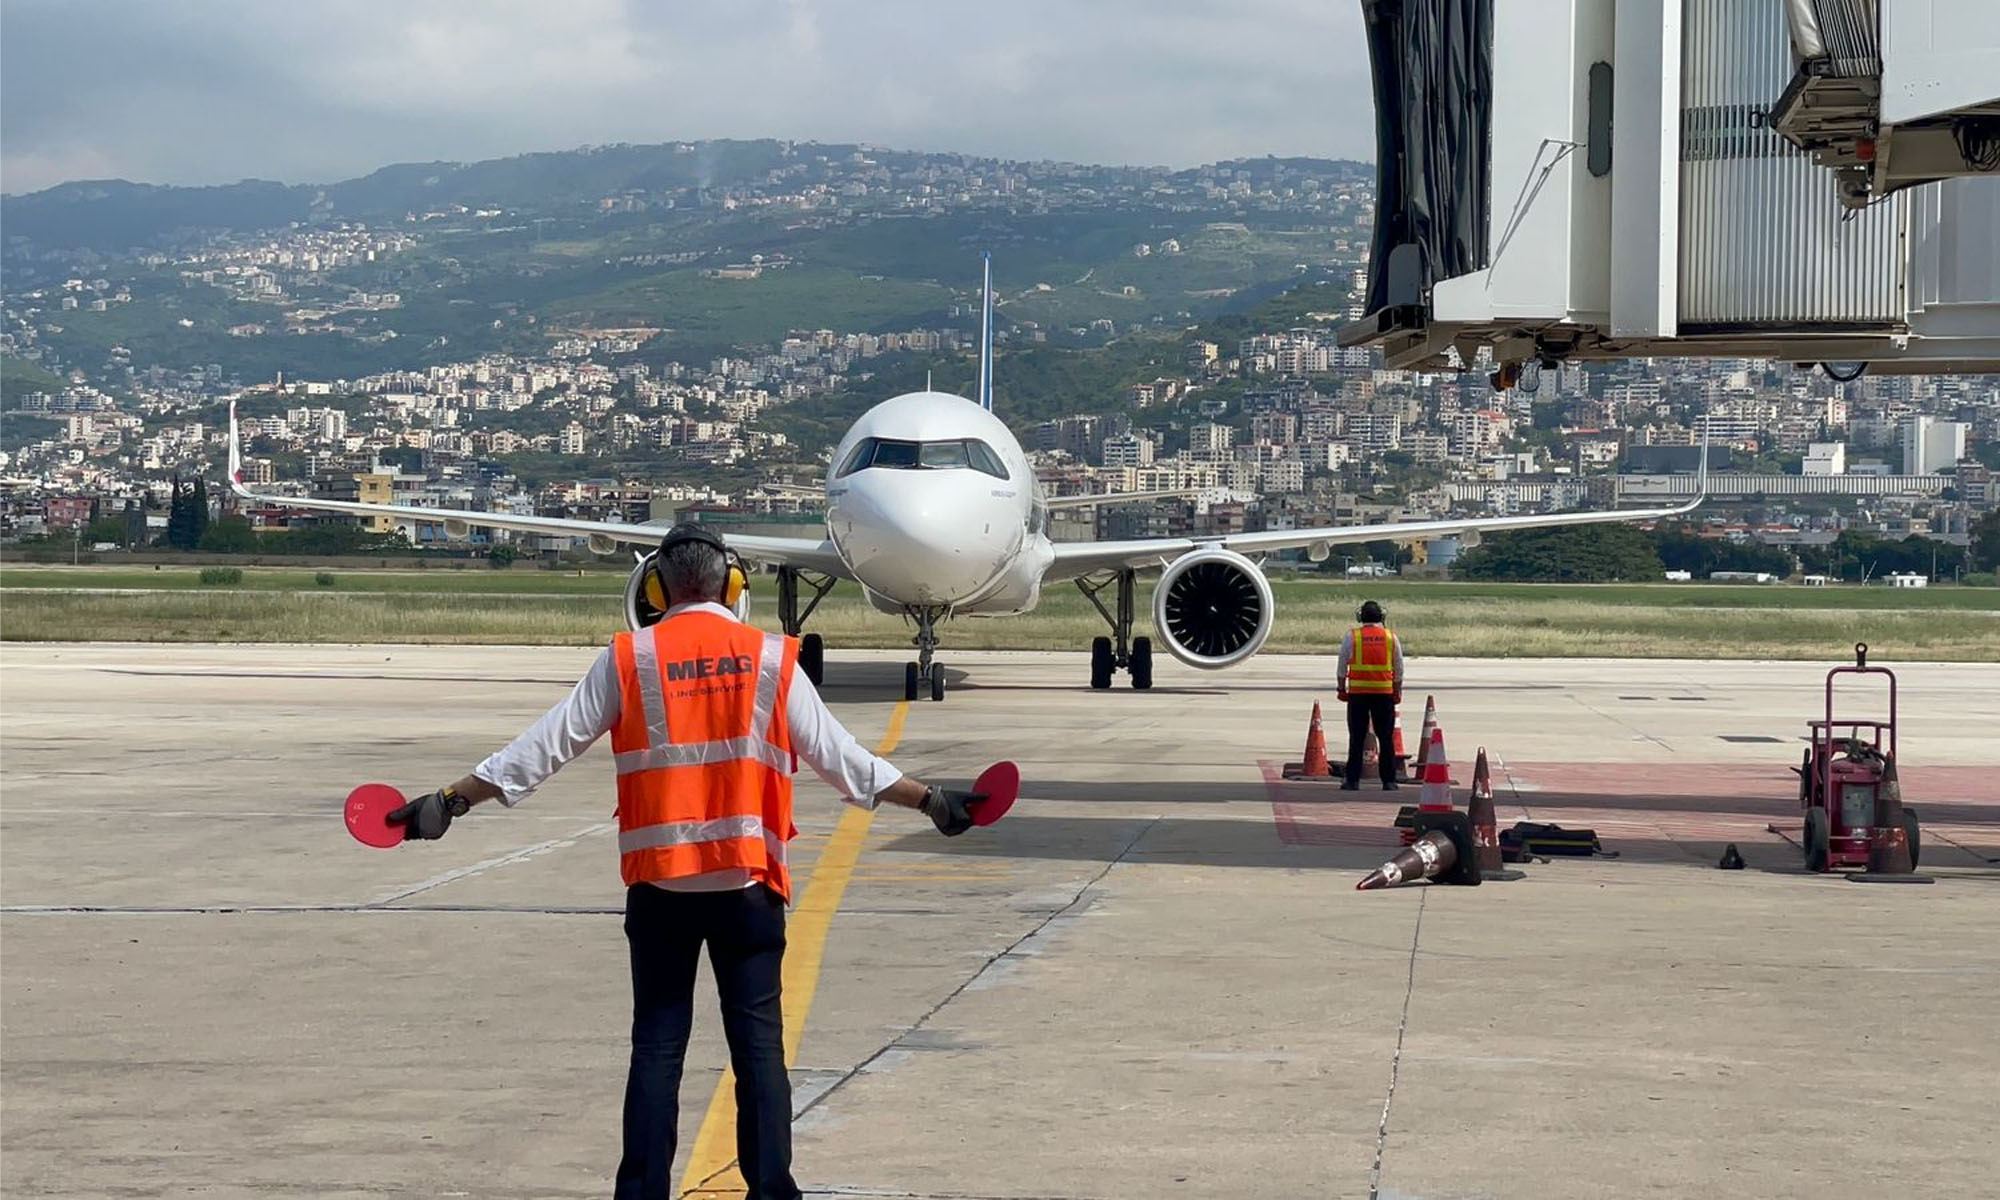
On Sunday evening, January 7, 2024, Beirut’s Rafic Hariri International Airport experienced a cyber attack that resulted in political messages appearing on its departure and arrival screens, disrupting normal flight information and temporarily halting luggage belt operations.
Lebanon’s Minister of Public Works and Transport, Ali Hamieh, addressed the public the following day, expressing a commitment to uncovering the perpetrators of the incident and reassuring the public that the airport remained fully operational.
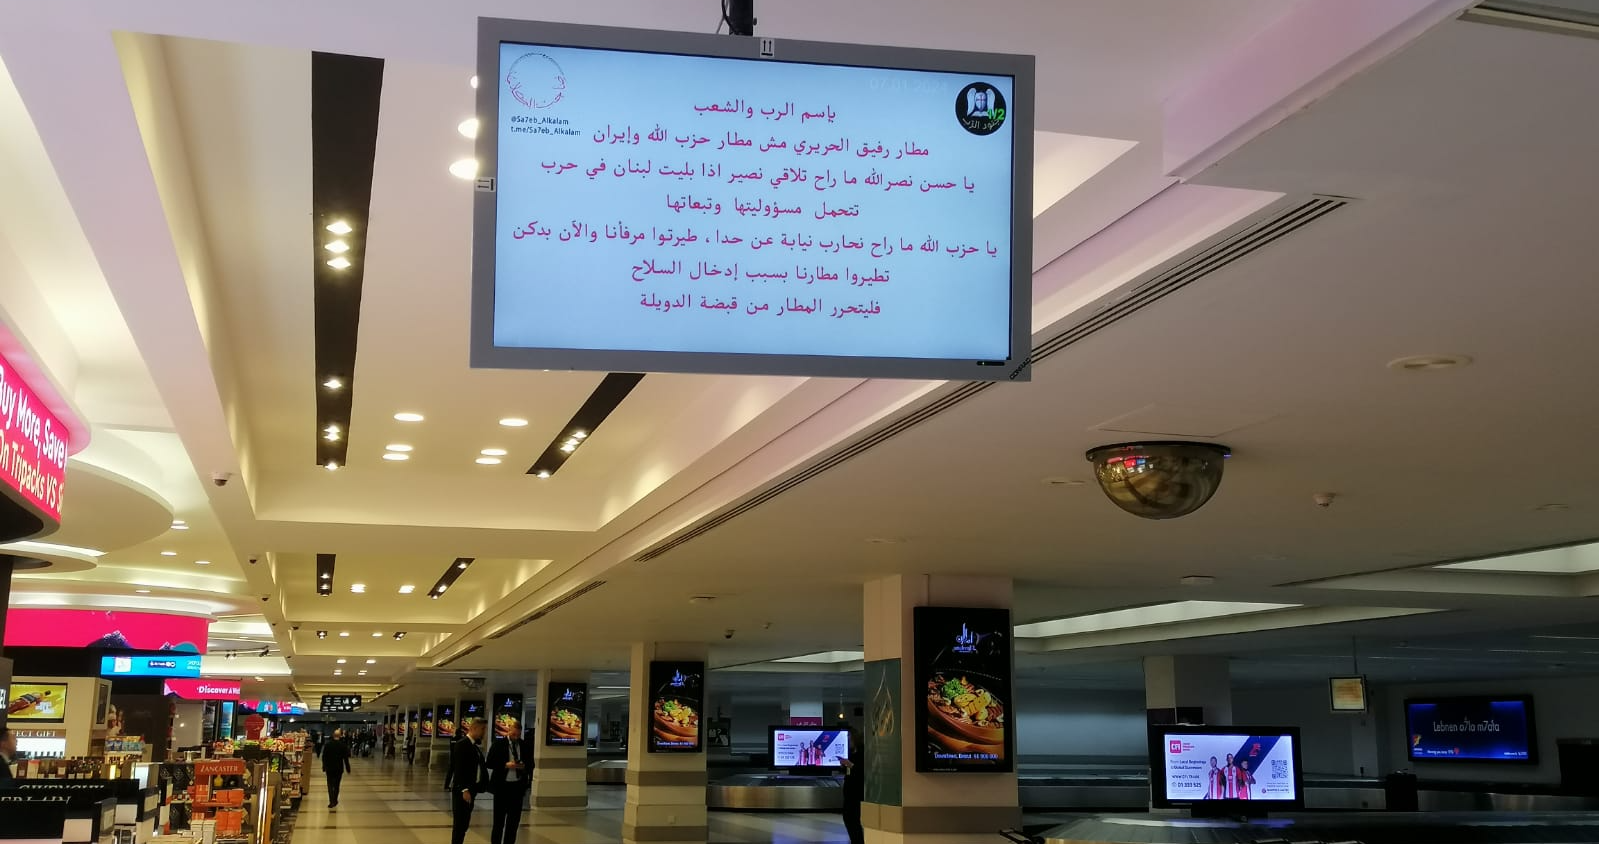
Meanwhile, Fadi El-Hassan, Director General of Civil Aviation, reported that the issues with the airport’s screens had been resolved, and normal functionality had been restored across passenger terminals, including arrival and departure halls.
Despite these developments, official statements from Lebanese authorities regarding the incident were yet to be released, as investigations continued under the oversight of the Lebanese security services, as confirmed by Minister Ali Hamieh.
As of now, no information has surfaced regarding the compromise of airport data, such as flight details, passenger records, or other sensitive information. However, technical experts at SMEX, a nonprofit organization dedicated to advancing digital human rights across West Asia and North Africa, say that the severity of the cyberattack reveals clues on the motives behind it.
Also Read: The Largest Data Breaches In The Middle East
Members of SMEX’s technical team raised concerns about the cyber breach, stating, “If the perpetrators were able to manipulate screen content and disrupt the Baggage Handling System (BHS), it indicates the possible presence of malware within the compromised system”.
SMEX’s technical experts have also outlined several conceivable scenarios for the attack:
- The breach may have originated from the airport’s internal network, possibly involving the installation of malicious software by an individual with insider access to the airport’s systems.
- Another possibility is the compromise of an employee’s device through social engineering or a phishing attack, typically delivered via email or other deceptive means.
- An employee with privileged system access might have been coerced or manipulated through blackmail, bribery, or threats, facilitating unauthorized entry into the airport’s systems.
Lebanese authorities have yet to pinpoint the root cause of the airport cyberattack, leaving room for speculation about potential sources, which may include internal, external, or even governmental actors.


News
ESET Bets On Specialized Security AI At 0.5% The Training Cost
ESET says NeoCortex can estimate an attacker’s next move, with a kill switch and human oversight built in to keep it from going rogue.

A sign-in anomaly, a suspicious process launch and an unusual connection may look harmless alone. Together, they can describe an intrusion that is hard for security to teams to piece together.
To solve that problem, ESET announced ESET NeoCortex on November 4, 2026: a specialized foundational AI model for cybersecurity. It powers ESET LiveCortex, available within the ESET PROTECT Platform, which connects fragmented security signals and turns them into actionable incidents.
Filtering is the main selling point, with LiveCortex processing billions of raw telemetry events daily, and just 0.00111% of them contributing to incidents presented to customers. The aim is less alert fatigue and more analyst time spent on threats that matter.
NeoCortex is built on world-model architecture, learning how digital environments behave and how events relate. ESET says that lets it reconstruct missing incident context, recognize similar past cases and estimate an attacker’s likely next step – what the company calls “minus-one-day defense,” a chance to intervene before the next stage unfolds. ESET points to Black October, the week leading up to October 25, 2026, when critical security issues affecting PHP, Linux, GitLab and other key systems demanded rapid, prioritized responses, as the kind of moment where that context matters.
ESET’s internal research also suggests a specialized model like NeoCortex can be trained at up to 200 times lower cost than a large general reasoning model, while delivering more accurate, defense-focused results. The company credits optimized training, a focus on cybersecurity vocabulary, lower computing requirements and privately owned hardware.
Also Read: Dubai Says Its Deepfake Detector Needs Just 7 Seconds Of Video
“AI is accelerating both cyberattacks and cyberdefenses. With ESET NeoCortex, we are applying our AI investment to develop specialized foundational cybersecurity intelligence that remains under our control and strengthens, rather than replaces, human expertise,” said Juraj Malcho, Chief Technology Officer at ESET.
As part of the design, NeoCortex forms part of a layered architecture combining specialized models, deterministic controls, correlation logic, validation, auditability and expert human oversight. Safeguards include restricted sandboxes, read-only tools, continuous monitoring, defined usage and token limits, a kill switch and human oversight of critical response decisions. The model is also developed and self-hosted on ESET’s own infrastructure, which the company says reduces exposure to shifts among third-party AI providers, including commercial and geopolitical ones.

ESET Bets On Specialized Security AI At 0.5% The Training Cost

Whish Money Opens A Montreal Flagship To Enter The Canadian Market

Abu Dhabi Is Making Its Rulebook Readable To AI, With OpenAI

Binance Reportedly Loses $6.3 Billion In Record Crypto Heist

Robinhood Receives Approval To Launch In The Middle East

G42’s Inception42 Wants AI To Show Its Work Before Investors Commit

Abu Dhabi’s Robot Kitchen Is Serving Up Biryani, Not Burgers

Shokz OpenDots 2 Review: Clip-On Audio Gets A Bass-Heavy Makeover

WHOOP Goes Arabic, Betting On The Gulf’s Appetite For Health Data

Sennheiser’s MOMENTUM 5 Series Bets On Batteries You Can Swap


-
 News3 weeks ago
Abu Dhabi’s Robot Kitchen Is Serving Up Biryani, Not Burgers
-
 Product Reviews3 weeks ago
Shokz OpenDots 2 Review: Clip-On Audio Gets A Bass-Heavy Makeover
-
 News3 weeks ago
Sennheiser’s MOMENTUM 5 Series Bets On Batteries You Can Swap
-
 News2 weeks ago
Checkout.com Reports 20% Higher Payment Acceptance For PRYPCO