News
Exploits In Microsoft Exchange Used To Breach Over 30,000 Organizations

Over 30,000 entities, including local governments, small businesses, defense contractors, and education institutions, have been breached because of unpatched exploits in Microsoft Exchange, reported journalist and investigative reporter Brian Krebs on his blog, KrebsOnSecurity.
“In each incident, the intruders have left behind a ‘web shell,’ an easy-to-use, password-protected hacking tool that can be accessed over the Internet from any browser. The web shell gives the attackers administrative access to the victim’s computer servers,” Krebs wrote.
According to Microsoft, the attack was orchestrated by notorious Chinese hacking group Hafnium, and they started on January 6th, the day when rioters stormed the United States Capitol in a violent attack against the 117th United States Congress.
Microsoft released emergency security updates to patch the vulnerabilities on March 2nd, which means that the attackers had nearly two months to infiltrate vulnerable systems. The tech giant has been working closely with the U.S. Cybersecurity & Infrastructure Security Agency (CISA), as well as other public and private organizations, to secure all unpatched servers running Exchange Server 2013, 2016, or 2019 (Exchange Online hasn’t been affected).
“The best protection is to apply updates as soon as possible across all impacted systems,” said Microsoft spokesperson in a written statement. “We continue to help customers by providing additional investigation and mitigation guidance. Impacted customers should contact our support teams for additional help and resources.”
Also Read: Dubai Police Use Futuristic Technology To Read Murder Suspect’s Mind
While most known victims of the attacks were located in the United States, breaches related to the Microsoft Exchange vulnerabilities were also detected on the other side of the Atlantic. For example, the Prague municipality and the Czech Ministry for Labor and Social Affairs were forced to shut down some of their systems and install emergency patches. No data was stolen during the attack, said Czech government officials.
Attacks like this one highlight the importance of timely patching and modern intrusion detection tools, which are able to detect unusual activity while it’s still time to act.


News
Microsoft Plans $10 Billion-Plus Gulf Expansion Despite Iran Conflict
Security is shaping Microsoft’s approach, from resilience work with governments to what it will say about how the money splits by country.

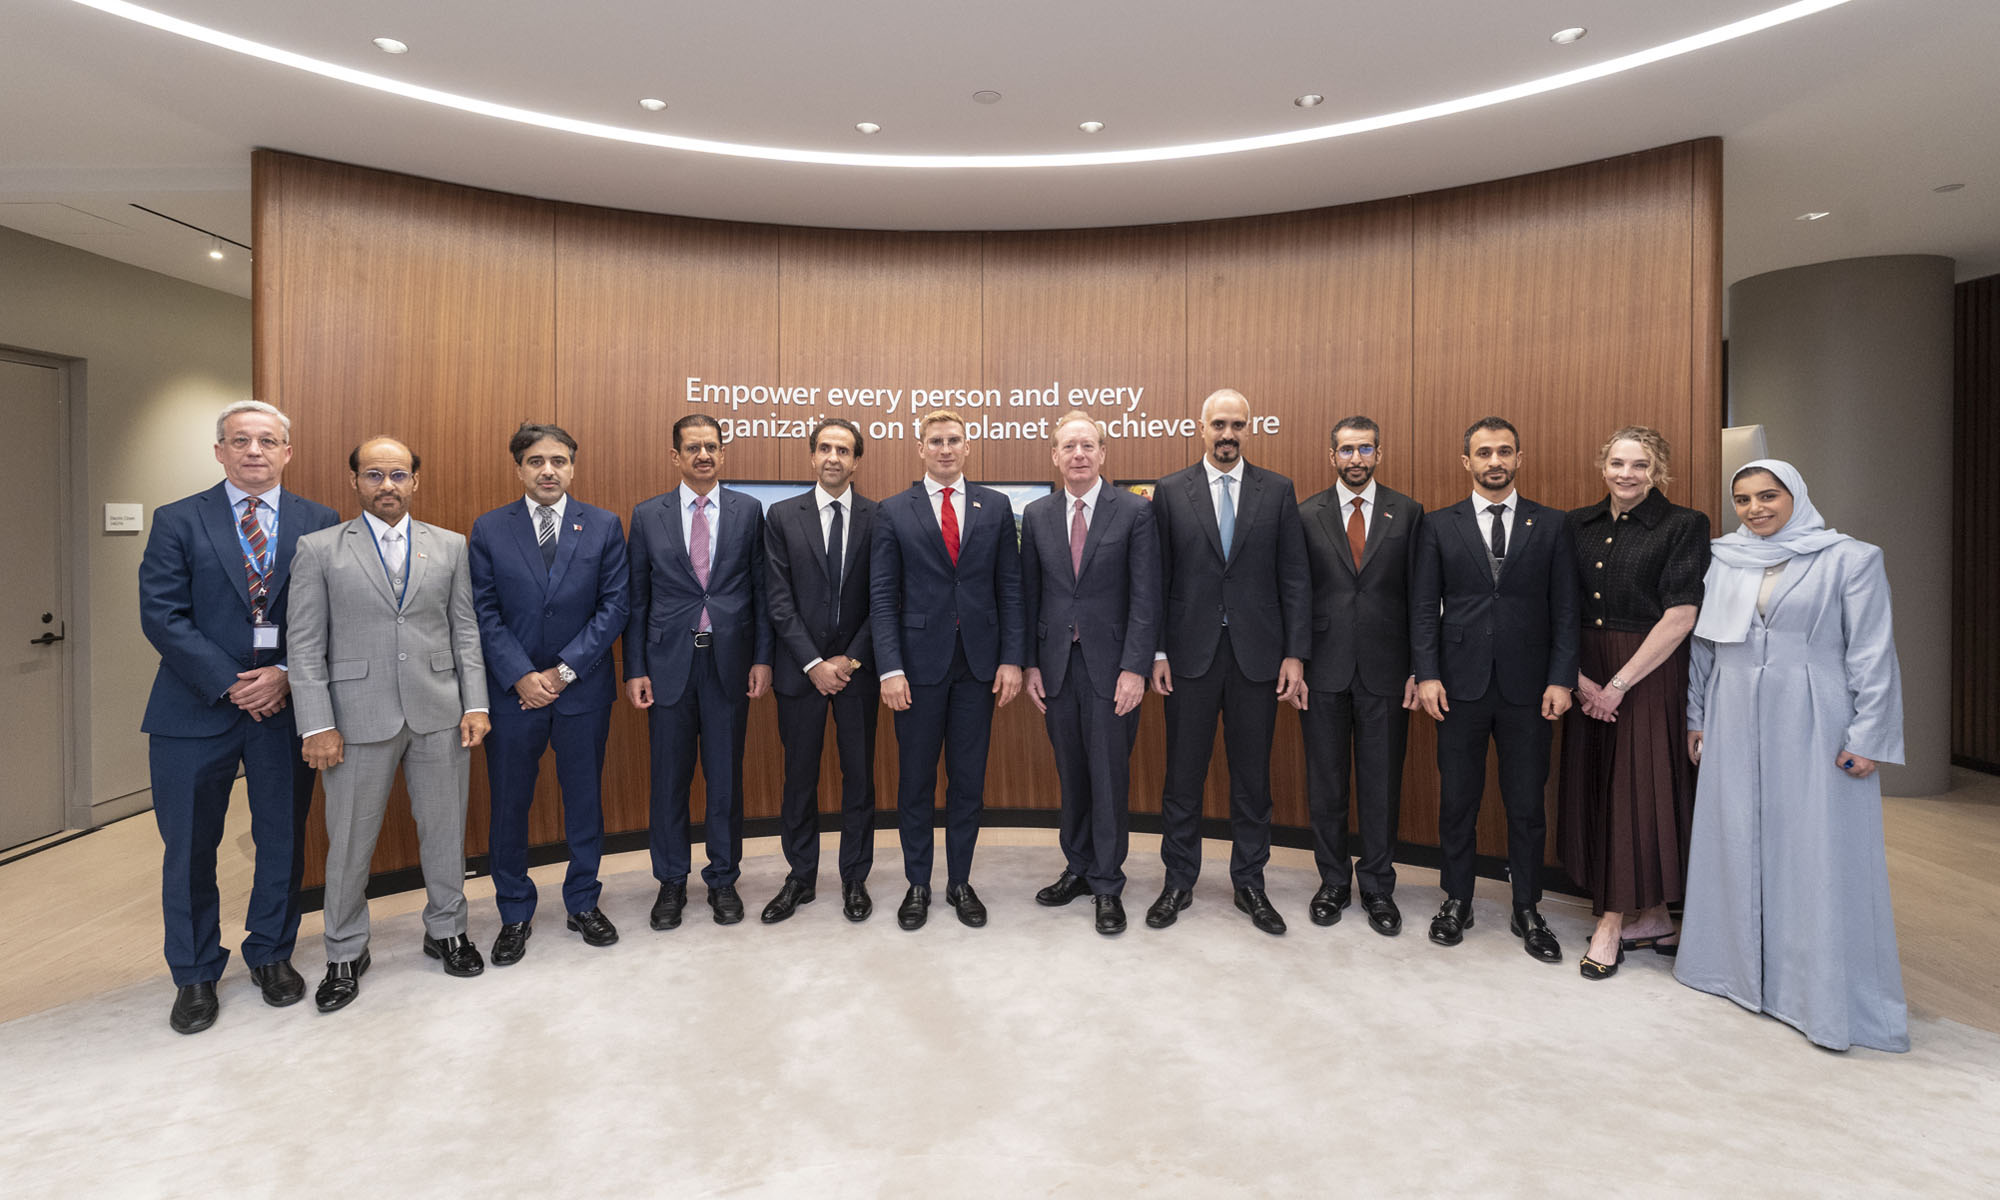
Microsoft is planning more than $10 billion of investment across the UAE, Saudi Arabia, Qatar and Kuwait through 2030, Vice Chair and President Brad Smith told Reuters, calling the spending schedule aggressive. The Iranian conflict that began on February 28 has not persuaded the company to scale back.
“We’re sustaining all the investments we planned to make before this conflict started, and we are in fact adding to them,” Smith said. The $10 billion-plus total does not, however, show how large those additions are.
The investment, which Smith described as part of Microsoft’s continued infrastructure expansion, is aimed at cloud and AI infrastructure and at the company’s growing regional operations. Microsoft also intends to put more than $400 million into subsea and terrestrial connectivity across the Middle East by 2030.
The spending fits the region’s own ambitions too. Gulf governments have been investing heavily in AI infrastructure as part of a push to diversify their economies beyond oil and gas and turn themselves into global technology hubs. Major cloud and AI providers have been drawn in part by the land and relatively low-cost energy on offer.
Microsoft is widening its partnerships with regional AI companies, though not on identical terms. In 2024, it invested $1.5 billion in Abu Dhabi-based G42 for a minority stake, and Smith currently sits on G42’s board. Saudi Arabia’s Humain and Qatar’s Qai are working with Microsoft on selected priority areas, but Smith said the company does not plan to make capital investments in either.
Also Read: Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power
The conflict has added another strand to Microsoft’s work in the region. Since it began, Smith said, the company has supported regional partners with digital resilience assessments, and it is now working with Gulf countries through a digital resilience initiative focused on preparedness and the protection of critical data.
So far, the company has given no country-by-country breakdown of the investment, citing security among other factors. So while the headline figure is public, how Microsoft divides the spending among the four countries is not.

Microsoft Plans $10 Billion-Plus Gulf Expansion Despite Iran Conflict

In Kuwait, Your Surgeon Might Be Operating From Another Country

Qatar Folds 45 State Companies Into A Single Investment Platform

Trip.com Is Betting An AI Agent Will Book Your Next Vacation

Meta’s New $499 Plan Puts A Price On Reaching A Real Person

Apple’s First Folding iPhone Arrives Late To A Shrinking Market
Trip.com Is Betting An AI Agent Will Book Your Next Vacation

Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power

OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA

Musk’s Boring Company Wants To Dig 150 KM Of Tunnel Under The UAE


-
 News3 weeks ago
Apple’s First Folding iPhone Arrives Late To A Shrinking Market
-
 News2 weeks ago
Trip.com Is Betting An AI Agent Will Book Your Next Vacation
-
 News2 weeks ago
Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power
-
 News2 weeks ago
OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA