News
Exploits In Microsoft Exchange Used To Breach Over 30,000 Organizations

Over 30,000 entities, including local governments, small businesses, defense contractors, and education institutions, have been breached because of unpatched exploits in Microsoft Exchange, reported journalist and investigative reporter Brian Krebs on his blog, KrebsOnSecurity.
“In each incident, the intruders have left behind a ‘web shell,’ an easy-to-use, password-protected hacking tool that can be accessed over the Internet from any browser. The web shell gives the attackers administrative access to the victim’s computer servers,” Krebs wrote.
According to Microsoft, the attack was orchestrated by notorious Chinese hacking group Hafnium, and they started on January 6th, the day when rioters stormed the United States Capitol in a violent attack against the 117th United States Congress.
Microsoft released emergency security updates to patch the vulnerabilities on March 2nd, which means that the attackers had nearly two months to infiltrate vulnerable systems. The tech giant has been working closely with the U.S. Cybersecurity & Infrastructure Security Agency (CISA), as well as other public and private organizations, to secure all unpatched servers running Exchange Server 2013, 2016, or 2019 (Exchange Online hasn’t been affected).
“The best protection is to apply updates as soon as possible across all impacted systems,” said Microsoft spokesperson in a written statement. “We continue to help customers by providing additional investigation and mitigation guidance. Impacted customers should contact our support teams for additional help and resources.”
Also Read: Dubai Police Use Futuristic Technology To Read Murder Suspect’s Mind
While most known victims of the attacks were located in the United States, breaches related to the Microsoft Exchange vulnerabilities were also detected on the other side of the Atlantic. For example, the Prague municipality and the Czech Ministry for Labor and Social Affairs were forced to shut down some of their systems and install emergency patches. No data was stolen during the attack, said Czech government officials.
Attacks like this one highlight the importance of timely patching and modern intrusion detection tools, which are able to detect unusual activity while it’s still time to act.


News
For etisalat, More Bandwidth Is A Matter Of Digital Sovereignty
The etisalat group plans to expand its international capacity from 20 Tbps to more than 500 Tbps by 2030, with new routes designed for speed and resilience.


By 2030, etisalat group plans to lift its international connectivity capacity to more than 500 terabits per second (Tbps), more than 25 times the 20 Tbps it has today. The group presented the expansion as preparation for rising AI demand and an important move for the UAE’s digital sovereignty.
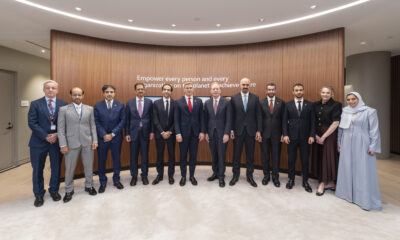
His Highness Sheikh Mansour bin Zayed Al Nahyan, Vice President, Deputy Prime Minister and Chairman of the Presidential Court, witnessed the launch of the project, which covers the UAE and international markets. Sheikh Mansour is also Chairman of the Emirates Investment Authority, etisalat group’s main shareholder.
He emphasized the role of coordinated national efforts in advancing the UAE’s AI and digital economy ambitions. “AI is a central pillar in our development journey moving forward,” he said, adding that developing the country’s digital capabilities would empower every institution, public and private, to build and innovate with AI “at the scale the coming decade will demand”.
“This project reflects our conviction that the UAE should not simply adopt AI, but govern it and build with it,” said H.E Jassem Mohamed Bu Ataba Alzaabi, Chairman of etisalat group. “That requires digital infrastructure at a scale that would prepare us for the future”. He cast greater international connectivity as a strategic answer to the challenges of processing and moving data globally.
Also Read: RØDE’s Low-Profile Studio Arm Is Designed To Stay Out Of Shot
Beyond raw bandwidth, the expansion will introduce new connectivity routes intended to improve reliability and efficiency, and Alzaabi tied them directly to the sovereignty goal. “Delivered through diversified routes and low-latency design, the project is set to keep the country’s connection to the global digital economy fast, direct and resilient, while ensuring the UAE’s digital sovereignty,” he said.
He also linked the plan to the group’s 50-year commitment to building infrastructure for the nation. The announcement didn’t mention what the expansion will cost. Nor did it name the new routes or say who will build them, the details that would show what digital sovereignty means in practice.

For etisalat, More Bandwidth Is A Matter Of Digital Sovereignty

NEOPAY Wants To Follow Merchants Across Channels And Borders

RØDE’s Low-Profile Studio Arm Is Designed To Stay Out Of Shot

Microsoft Plans $10 Billion-Plus Gulf Expansion Despite Iran Conflict

In Kuwait, Your Surgeon Might Be Operating From Another Country

Trip.com Is Betting An AI Agent Will Book Your Next Vacation

Musk’s Boring Company Wants To Dig 150 KM Of Tunnel Under The UAE

OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA

Apple’s First Folding iPhone Arrives Late To A Shrinking Market

Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power


-
 News3 weeks ago
Trip.com Is Betting An AI Agent Will Book Your Next Vacation
-
 News3 weeks ago
Musk’s Boring Company Wants To Dig 150 KM Of Tunnel Under The UAE
-
 News3 weeks ago
OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA
-
 News3 weeks ago
Meta’s New $499 Plan Puts A Price On Reaching A Real Person