News
How Adversarial ML Can Turn An ML Model Against Itself
Discover the main types of adversarial machine learning attacks and what you can do to protect yourself.

Machine learning (ML) is at the very center of the rapidly evolving artificial intelligence (AI) landscape, with applications ranging from cybersecurity to generative AI and marketing. The data interpretation and decision-making capabilities of ML models offer unparalleled efficiency when you’re dealing with large datasets. As more and more organizations implement ML into their processes, ML models have emerged as a prime target for malicious actors. These malicious actors typically attack ML algorithms to extract sensitive data or disrupt operations.
What Is Adversarial ML?
Adversarial ML refers to an attack where an ML model’s prediction capabilities are compromised. Malicious actors carry out these attacks by either manipulating the training data that is fed into the model or by making unauthorized alterations to the inner workings of the model itself.
How Is An Adversarial ML Attack Carried Out?
There are three main types of adversarial ML attacks:
Data Poisoning
Data poisoning attacks are carried out during the training phase. These attacks involve infecting the training datasets with inaccurate or misleading data with the purpose of adversely affecting the model’s outputs. Training is the most important phase in the development of an ML model, and poisoning the data used in this step can completely derail the development process, rendering the model unfit for its intended purpose and forcing you to start from scratch.
Evasion
Evasion attacks are carried out on already-trained and deployed ML models during the inference phase, where the model is put to work on real-world data to produce actionable outputs. These are the most common form of adversarial ML attacks. In an evasion attack, the attacker adds noise or disturbances to the input data to cause the model to misclassify it, leading it to make an incorrect prediction or provide a faulty output. These disturbances are subtle alterations to the input data that are imperceptible to humans but can be picked up by the model. For example, a car’s self-driving model might have been trained to recognize and classify images of stop signs. In the case of an evasion attack, a malicious actor may feed an image of a stop sign with just enough noise to cause the ML to misclassify it as, say, a speed limit sign.
Model Inversion
A model inversion attack involves exploiting the outputs of a target model to infer the data that was used in its training. Typically, when carrying out an inversion attack, an attacker sets up their own ML model. This is then fed with the outputs produced by the target model so it can predict the data that was used to train it. This is especially concerning when you consider the fact that certain organizations may train their models on highly sensitive data.
How Can You Protect Your ML Algorithm From Adversarial ML?
While not 100% foolproof, there are several ways to protect your ML model from an adversarial attack:
Validate The Integrity Of Your Datasets
Since the training phase is the most important phase in the development of an ML model, it goes without saying you need to have a very strict qualifying process for your training data. Make sure you’re fully aware of the data you’re collecting and always make sure to verify it’s from a reliable source. By strictly monitoring the data that is being used in training, you can ensure that you aren’t unknowingly feeding your model poisoned data. You could also consider using anomaly detection techniques to make sure the training datasets do not contain any suspicious samples.
Secure Your Datasets
Make sure to store your training data in a highly secure location with strict access controls. Using cryptography also adds another layer of security, making it that much harder to tamper with this data.
Train Your Model To Detect Manipulated Data
Feed the model examples of adversarial inputs that have been flagged as such so it will learn to recognize and ignore them.
Perform Rigorous Testing
Keep testing the outputs of your model regularly. If you notice a decline in quality, it might be indicative of an issue with the input data. You could also intentionally feed malicious inputs to detect any previously unknown vulnerabilities that might be exploited.
Adversarial ML Will Only Continue To Develop
Adversarial ML is still in its early stages, and experts say current attack techniques aren’t highly sophisticated. However, as with all forms of tech, these attacks will only continue to develop, growing more complex and effective. As more and more organizations begin to adopt ML into their operations, now’s the right time to invest in hardening your ML models to defend against these threats. The last thing you want right now is to lag behind in terms of security in an era when threats continue to evolve rapidly.
News
Microsoft Plans $10 Billion-Plus Gulf Expansion Despite Iran Conflict
Security is shaping Microsoft’s approach, from resilience work with governments to what it will say about how the money splits by country.

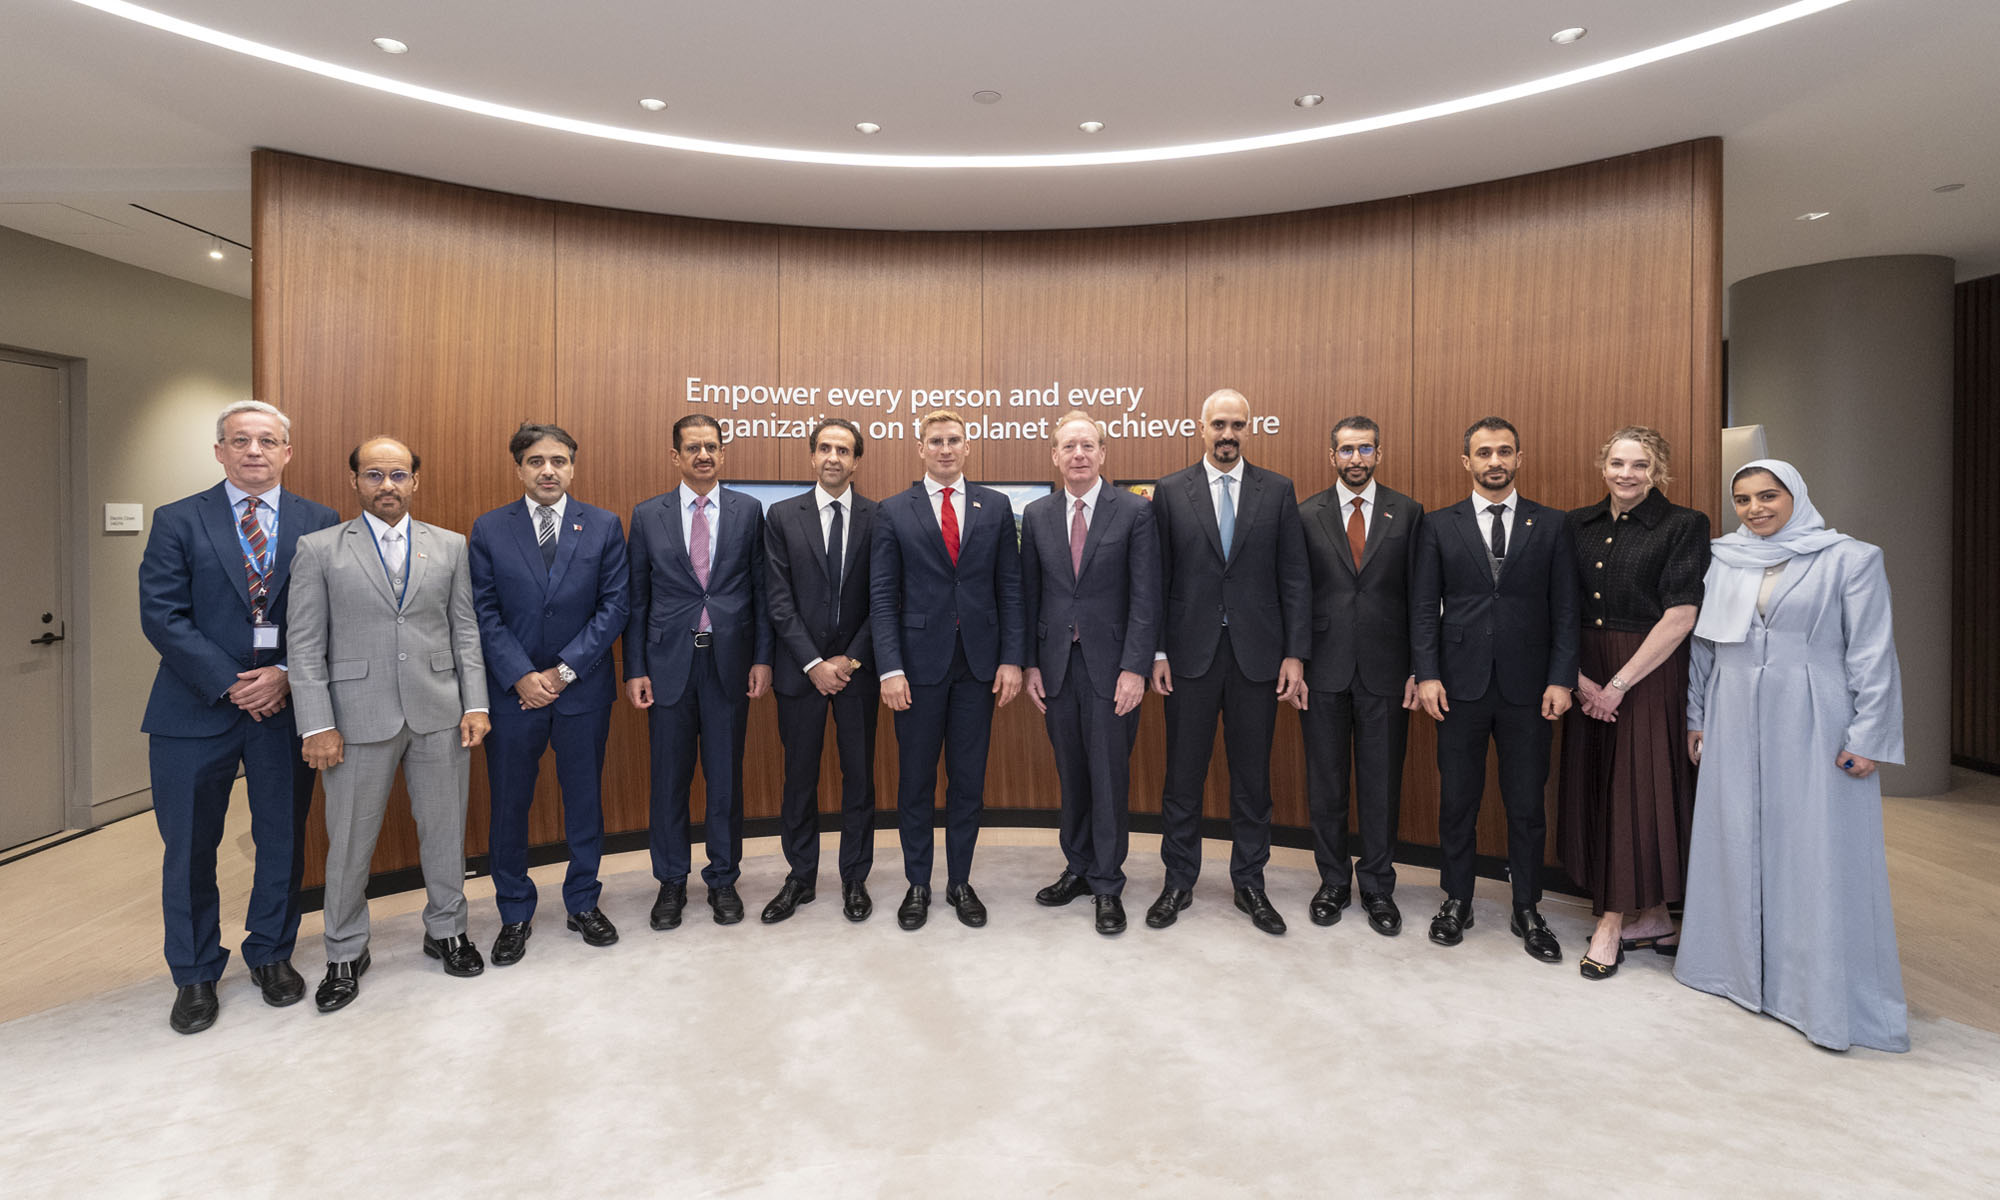
Microsoft is planning more than $10 billion of investment across the UAE, Saudi Arabia, Qatar and Kuwait through 2030, Vice Chair and President Brad Smith told Reuters, calling the spending schedule aggressive. The Iranian conflict that began on February 28 has not persuaded the company to scale back.
“We’re sustaining all the investments we planned to make before this conflict started, and we are in fact adding to them,” Smith said. The $10 billion-plus total does not, however, show how large those additions are.
The investment, which Smith described as part of Microsoft’s continued infrastructure expansion, is aimed at cloud and AI infrastructure and at the company’s growing regional operations. Microsoft also intends to put more than $400 million into subsea and terrestrial connectivity across the Middle East by 2030.
The spending fits the region’s own ambitions too. Gulf governments have been investing heavily in AI infrastructure as part of a push to diversify their economies beyond oil and gas and turn themselves into global technology hubs. Major cloud and AI providers have been drawn in part by the land and relatively low-cost energy on offer.
Microsoft is widening its partnerships with regional AI companies, though not on identical terms. In 2024, it invested $1.5 billion in Abu Dhabi-based G42 for a minority stake, and Smith currently sits on G42’s board. Saudi Arabia’s Humain and Qatar’s Qai are working with Microsoft on selected priority areas, but Smith said the company does not plan to make capital investments in either.
Also Read: Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power
The conflict has added another strand to Microsoft’s work in the region. Since it began, Smith said, the company has supported regional partners with digital resilience assessments, and it is now working with Gulf countries through a digital resilience initiative focused on preparedness and the protection of critical data.
So far, the company has given no country-by-country breakdown of the investment, citing security among other factors. So while the headline figure is public, how Microsoft divides the spending among the four countries is not.

Microsoft Plans $10 Billion-Plus Gulf Expansion Despite Iran Conflict

In Kuwait, Your Surgeon Might Be Operating From Another Country

Qatar Folds 45 State Companies Into A Single Investment Platform

Trip.com Is Betting An AI Agent Will Book Your Next Vacation

Meta’s New $499 Plan Puts A Price On Reaching A Real Person

Apple’s First Folding iPhone Arrives Late To A Shrinking Market
Trip.com Is Betting An AI Agent Will Book Your Next Vacation

Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power

OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA

Apple’s Latest Product Releases Make The Headlines


-
 News3 weeks ago
Apple’s First Folding iPhone Arrives Late To A Shrinking Market
-
 News2 weeks ago
Trip.com Is Betting An AI Agent Will Book Your Next Vacation
-
 News2 weeks ago
Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power
-
 News2 weeks ago
OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA