News
Google Chrome Exploit Results In Attack On Lebanese Journalists
According to antivirus company Avast, there is evidence that an Israeli spyware firm called Candiru used a vulnerability in Google Chrome to spy on journalists in Lebanon.

In early July 2022, Google patched a previously unknown vulnerability in its Chrome browser, known as CVE-2022-2294. The zero-day Chrome exploit only came to light after it was apparently used to spy on journalists in Lebanon.
Antivirus company, Avast, collated a report, which it delivered to Google detailing the zero-day exploit. In this report, Avast claims that Israeli spyware firm, Candiru, used the exploit to install spyware on the journalist’s computers.
It equally believes that the firm has used similar exploits to target Avast users in Turkey, Lebanon, Palestine and Yemen beginning in March of this year.
A zero-day exploit is, in short, a vulnerability in a piece of software that is unknown to the developers. They are typically discovered in the wild for this reason, and are known as zero-day because the developers have zero days in which to address the issue. This is because the vulnerability has the potential to cause damage from the moment it is discovered.
Avast alleges that Candiru used the above-mentioned exploit to gain access to user’s computers. It is believed to have compromised a website, which it used to redirect users to a server that could collect their data. If the data – collected on 50 data points such as location, language, time zone, etc. – met their requirements, the server would establish an encrypted channel.
Despite not claiming responsibility, Candiru is the prime suspect in the attack because the CVE-2022-2294 exploit was used to install the DevilsTongue spyware. This is a piece of malware previously linked to the group by Microsoft in a separate string of attacks.
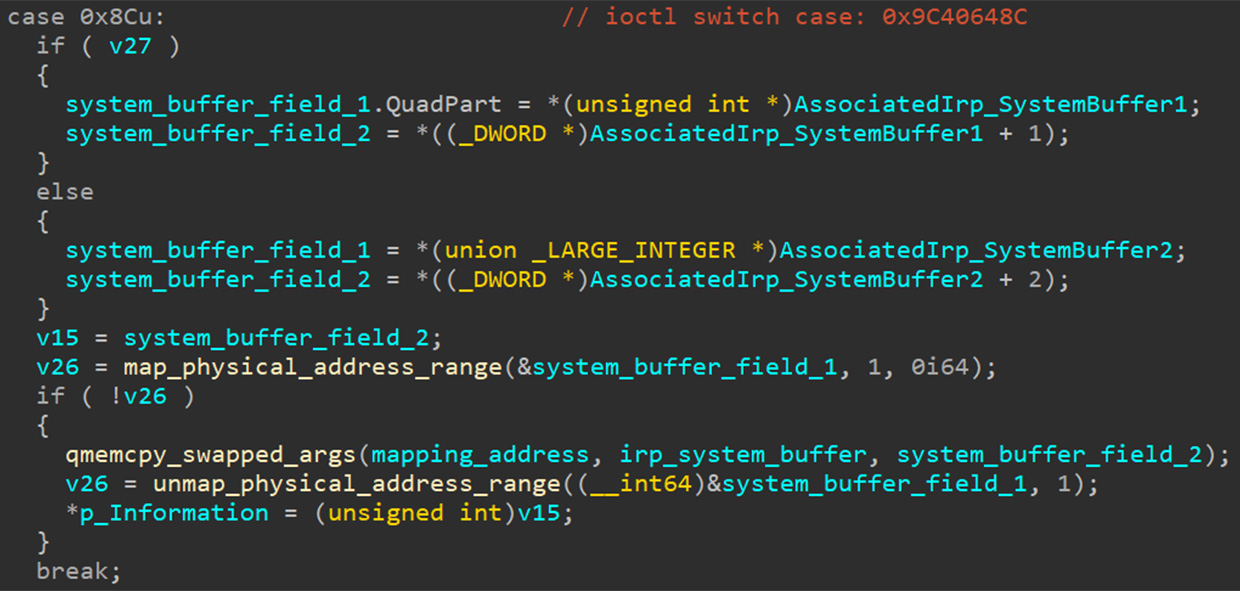
In its report, Avast claims that the zero-day exploit was used alongside another vulnerability capable of bypassing the sandbox security function in Chromium. However, Avast has (as yet) been unable to determine the second exploit used by the alleged attackers.
Also Read: DDoS Attacks Are A Growing Threat In Gaming
Luckily, Google released a patch for the exploit on July 4. As such, there is no need for Chrome users to be concerned, providing browsers are kept up to date. Microsoft and Apple have released patches for their Edge and Safari browsers, too, as they also use WebRTC.
Candiru has not yet been officially connected to the incident, so its involvement is currently (albeit well-informed) speculation. However, the tools used and computers targeted matches its previous spyware attempts dating from 2021 and early 2022. As the company has no public online presence, this fact is unlikely to change anytime soon.



News
NEOPAY Wants To Follow Merchants Across Channels And Borders
A controlling 65% stake in noon payments would give NEOPAY access to marketplace sellers, online merchants and the payment flows they generate.

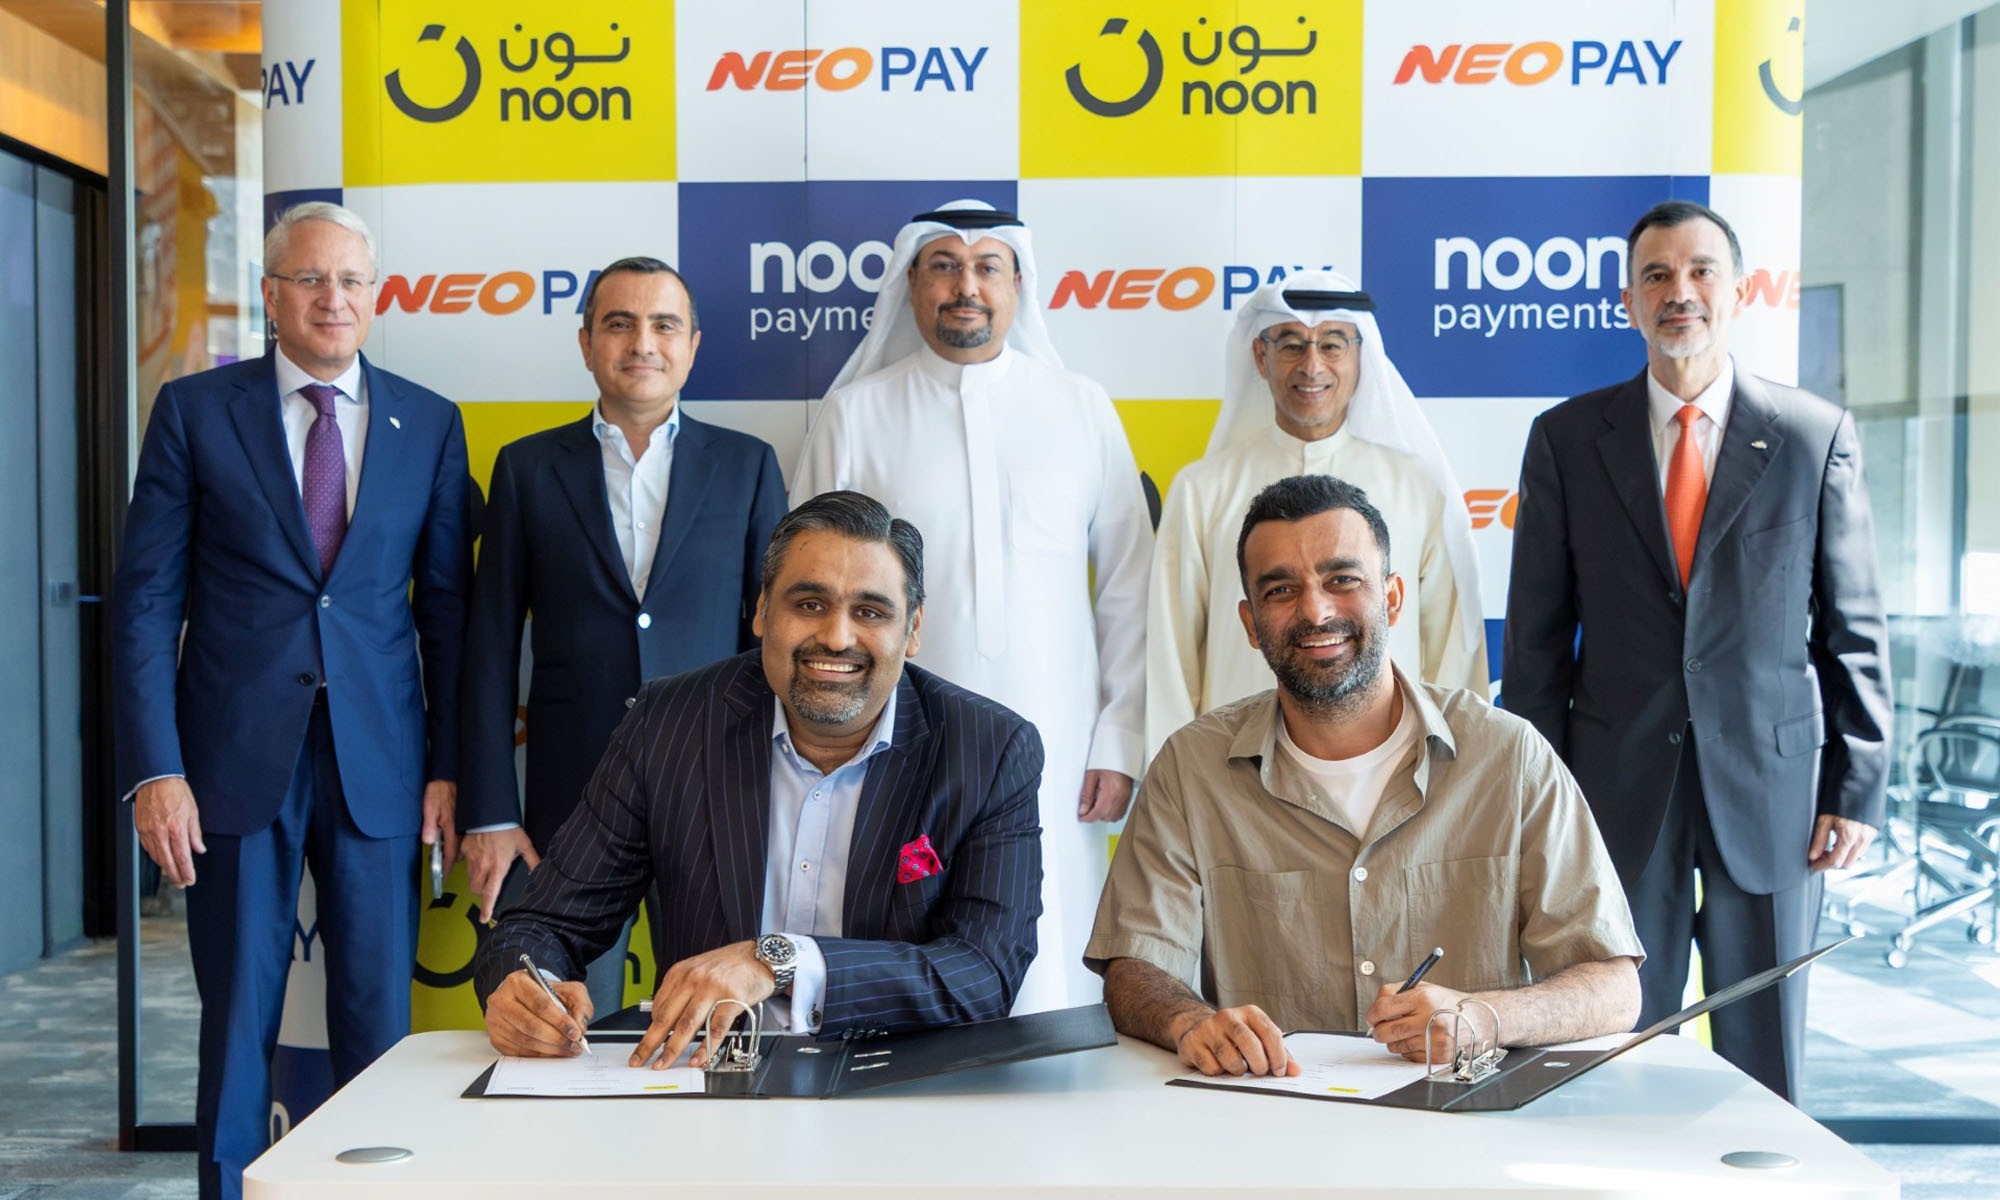
It’s been a long time since checkouts were single defined places. A merchant might take payments at a physical register, on its own website and through an online marketplace, sometimes in more than one country. NEOPAY wants to follow those transactions wherever they happen.
The UAE payments company has entered into an agreement to acquire a 65% controlling stake in noon payments. NEOPAY already runs the acquiring infrastructure that lets merchants accept card payments, along with omnichannel acceptance and a merchant services platform. This new deal would add noon payments’ embedded payments platform, e-commerce gateway and merchant network across the UAE, Saudi Arabia and Egypt. That would considerably expand both NEOPAY’s digital commerce capabilities and its regional reach.
For merchants, the attraction is a single provider for online and in-store payments, plus faster settlements, data and analytics, and value-added financial services.
“Payments should be simple, reliable, and built for the markets they serve,” said Faraz Khalid, CEO of noon. His counterpart at NEOPAY, Vibhor Mundhada, added: “We have built a strong payments business in the UAE, and our ambition is now to take that capability across the region”. The acquisition, Mundhada added, would “expand our footprint into Saudi Arabia and Egypt” while reinforcing NEOPAY’s position at home.
Also Read: In Kuwait, Your Surgeon Might Be Operating From Another Country
NEOPAY is also keen to point out potential payment volume increases. The company says noon payments’ integrations with marketplace sellers and online merchants create high transaction density in some of the region’s fastest-growing digital commerce segments. It also believes control of the business would give it access to those merchant relationships and payment flows, and speed up the rollout of alternative payment methods and installment options.
The combined roadmap targets faster merchant onboarding, better payment performance, tighter fraud controls and embedded financial services. The deal could also strengthen cross-border payments and settlement along key regional commerce corridors.

NEOPAY Wants To Follow Merchants Across Channels And Borders

RØDE’s Low-Profile Studio Arm Is Designed To Stay Out Of Shot

Microsoft Plans $10 Billion-Plus Gulf Expansion Despite Iran Conflict

In Kuwait, Your Surgeon Might Be Operating From Another Country

Qatar Folds 45 State Companies Into A Single Investment Platform

Trip.com Is Betting An AI Agent Will Book Your Next Vacation

Apple’s First Folding iPhone Arrives Late To A Shrinking Market

Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power

Musk’s Boring Company Wants To Dig 150 KM Of Tunnel Under The UAE

OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA


-
 News3 weeks ago
Trip.com Is Betting An AI Agent Will Book Your Next Vacation
-
 News3 weeks ago
Egypt’s Mobile Wallets Are Booming, But Cash Still Has Power
-
 News3 weeks ago
Musk’s Boring Company Wants To Dig 150 KM Of Tunnel Under The UAE
-
 News3 weeks ago
OKX Bets Streaming Perks Can Take Crypto Mainstream Across MENA